NIS2
Essential and important entities have to manage cyber risk, and their directors are personally accountable.
- Access control & asset policies
- Multi-factor authentication
- HR security: joiners, movers, leavers
We make sure people only have the access they need, and lose it the day they leave. That goes for employees, admins and service accounts, with an audit trail ready for NIS2 and DORA.
Be honest. Your answers stay in your browser.
Essential and important entities have to manage cyber risk, and their directors are personally accountable.
Banks, insurers and their ICT suppliers have to be able to prove who has access to what.
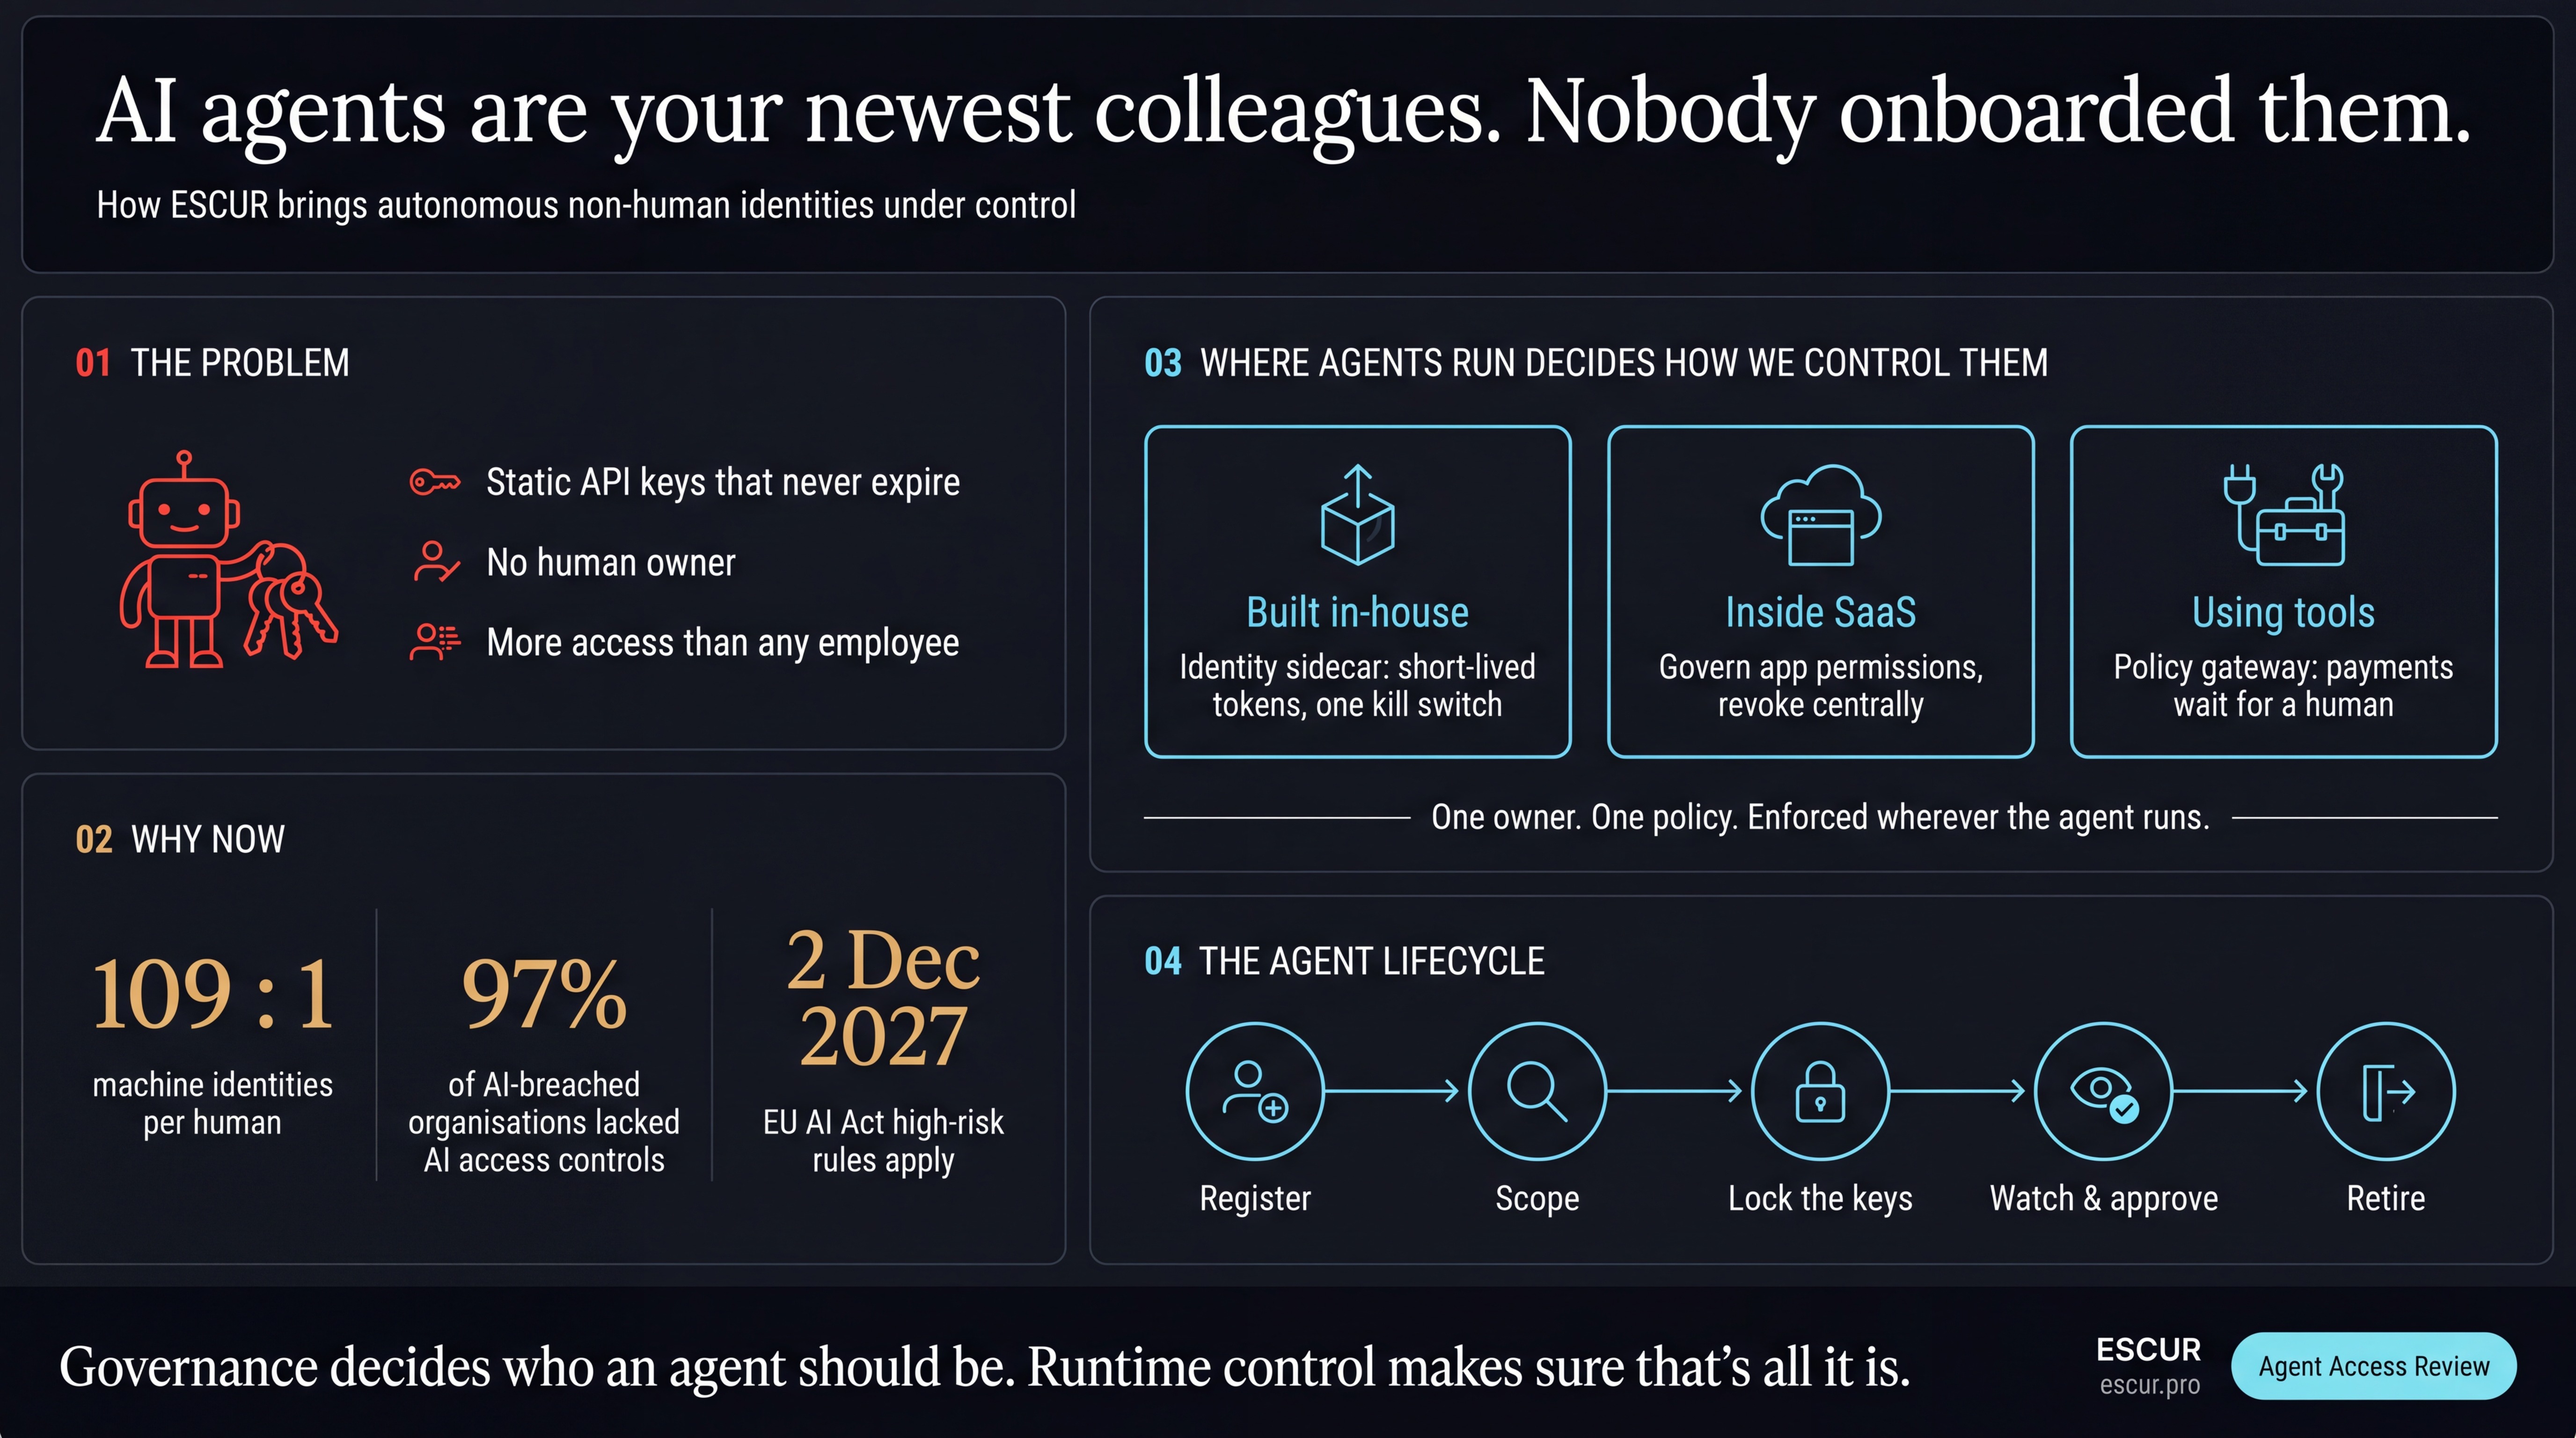
Companies are giving AI agents access to real systems. Each agent is an identity, and somebody has to own it.
AI agents read your mail, move money, open tickets and change systems. Each one logs in. Most have more access than any employee, no owner, and no end date.
Machine identities per human in the average organisation. Agents are the fastest-growing group.1
of organisations hit by an AI-related breach had no proper access controls on their AI.2
High-risk AI Act rules apply. Human oversight and logging have to be provable. NIS2 and DORA already cover these accounts today.3
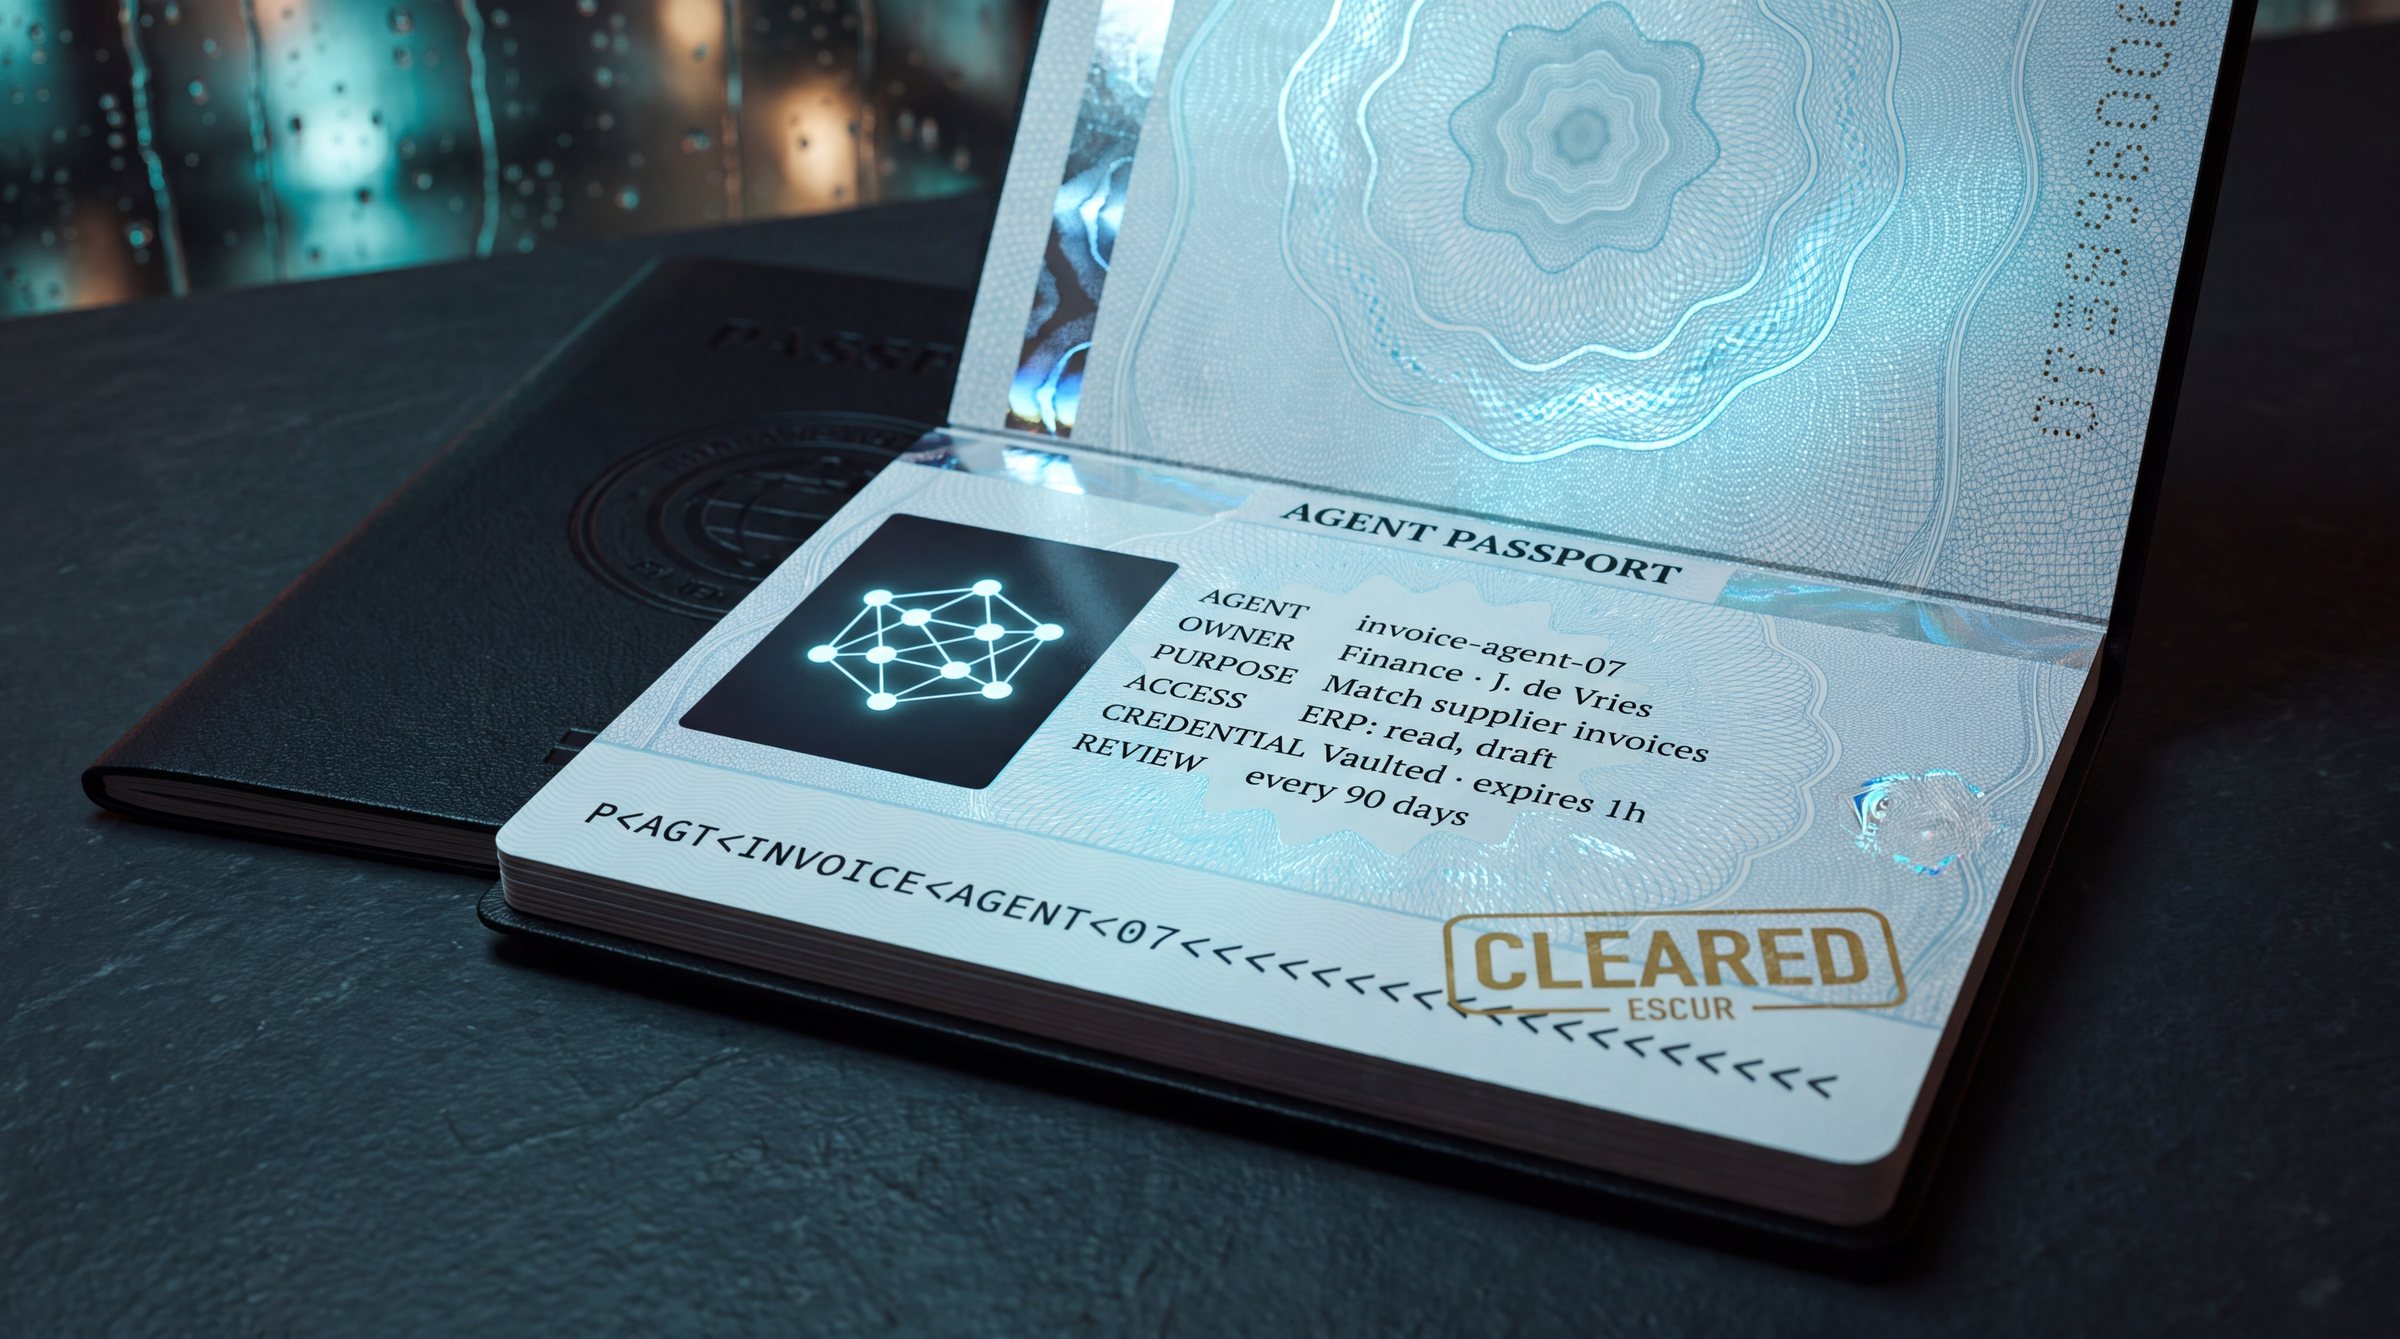
One record per agent: owner, purpose, allowed actions, credential, expiry and review. The rule is simple. No passport, no access.
Every agent gets a named human owner and a purpose. Nobody wants to sign for it? Then it gets switched off.
The passport lists the allowed systems and actions. Nothing more, and no standing admin rights.
No passwords or API keys in code. Short-lived tokens from a vault, rotated automatically.
Every action is logged against the passport. Payments, deletions and data exports wait for a human.
Every passport has an end date. The owner renews it at review, or the agent stops.
Wherever the agent runs, it has to show its passport.
Sits next to each agent you build. Short-lived tokens, and one switch to cut it off.
Copilot, Agentforce, ServiceNow. Their permissions follow the passport and are revoked centrally.
MCP servers and APIs are checked against the passport. Payments wait for a human.
Agent Passport Sprint
We find every agent, issue a passport for each one, and flag the ones nobody will sign for. Those are the first to switch off.
Why ESCUR. The passports live in One Identity, with the same joiner, mover, leaver and review discipline we’ve run for tens of thousands of human identities. Governance and enforcement from one place, run from the EU.
Find every account, including the ones nobody remembers creating.
Automate joiner-mover-leaver, roles and recertification on One Identity.
Vault privileged access, record sessions, stop sensitive data leaving.
We run it 24/7 and pull the audit evidence whenever you need it.
“Most breaches I’ve seen didn’t need a genius. They needed one account nobody switched off.”

Role management and process-driven authorisation.
Identity & role management across Western Continental Europe.
Best practice in IAM implementation and delivery.
One Identity Silver Partner. Forcepoint partner. EU-based.
Silver Partner for Identity Manager and Safeguard.
Data Loss Prevention & DSPM.
IGA foundation hosted and run on Azure.
ESCUR Ltd, registered in Bulgaria.
Senior IAM developers, one time zone from you.
Where most of our clients are.
Half an hour on a call. We’ll look at where your identity risk is and what your auditor is likely to ask first.